



Written by: David Christopher
Compiled by: Block unicorn

Block unicorn
Block unicorn
If there is a lack of accountability mechanisms, it could negatively impact the overall development of x402.
The success of x402 depends on native integrators. Unauthorized wrappers risk turning potential partners into adversaries.
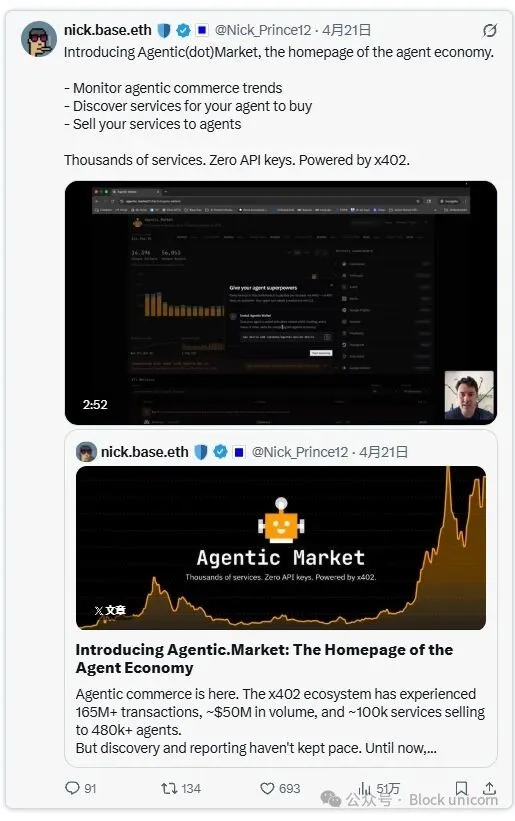
Last week, Coinbase launched agentic.market, a platform showcasing x402 endpoints aimed at making the x402 ecosystem more discoverable.
Browsing agentic.market, you'll find real-time, on-demand access to a variety of services, ranging from on-chain tools to mainstream APIs. Some endpoints are provided directly by the original providers. Many others come from third parties: companies that have wrapped existing APIs into x402 (and/or MPP) and packaged them into toolkits for agents, charging users a small fee for single-connection access.
The second approach complicates matters. Among the third-party endpoints showcased on Agentic Market are services from Wolfram Alpha, Google Flights, and Amadeus (a widely used travel data platform). I focus on these three because none of them have announced x402 integrations themselves, and their terms of service suggest they are unlikely to authorize third parties to build integrations on their behalf.
Every endpoint indexed on Agentic Market could be first-party (the original provider directly offering its API), authorized third-party (a reseller with explicit permission, typically through a formal certification or partnership program), or unauthorized third-party (a company reselling its paid API access without permission).
Across the marketplace, and across the broader x402 ecosystem, we cannot immediately distinguish which are first-party and which are third-party. Many endpoints appear to fall into the last category.
Contractual Terms
As noted, the terms of these three providers make unauthorized third-party arrangements seem highly probable, and in some cases, they completely rule out other options.
Wolfram Alpha explicitly prohibits "dealers and aggregators," bans any form of data scraping or mining, and forbids selling or sublicensing services without permission. These terms appear to leave no room for an authorized third-party path. Moreover, looking at the quick-start guide for this endpoint, it is clear this is not a first-party integration.
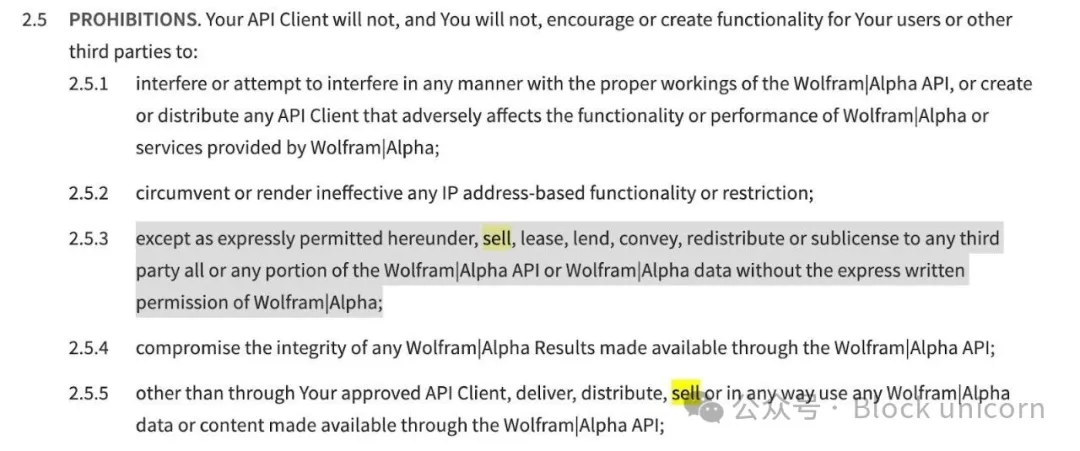
Prohibited API Content from Wolfram Alpha Terms of Service
Amadeus's master subscription services agreement only permits customers to access its services for internal business purposes and prohibits any "rental, lease, distribution, sale, resale, transfer, or other conveyance" of its access. Any third-party connection requires Amadeus's certification and must be recorded as a formal service order. This means this is the only way to obtain third-party authorization, and whether any existing endpoint complies with this requirement cannot be verified externally.
Restrictions in the Agreement: Restrictions from the Amadeus Master Subscription Services Agreement
Google's case is the most typical. Google Flights does not have a public API, and Google has strict protections for its data.
However, third-party wrappers are packaging access to Google Flights data, sourced from SerpApi—a company that Google is actively suing for scraping search results and reselling access. Google's complaint alleges that SerpApi developed tools to bypass access controls, sends "hundreds of millions" of fake requests daily for scraping, and resells copyrighted content embedded in search results.
Thus, Google is suing SerpApi for reselling copyrighted content and bypassing its access controls. Meanwhile, SerpApi's services are being wrapped by an agent toolkit provider, which offers them to agents for a fee. This is worth pondering.
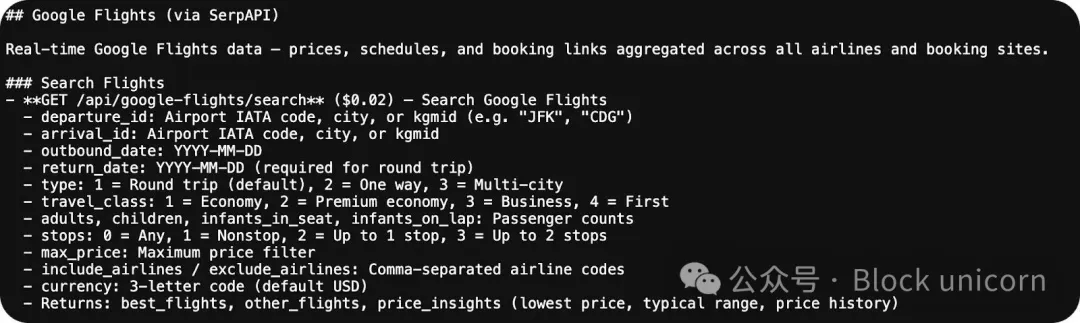
Details of accessing SerpApi via the StableTravel endpoint
How Compliance Manifests
You don't need a legal expert to see that these dynamics are "intricate." The good news is that a clearer model already exists.
MPP is the agent payment protocol launched by Tempo with its mainnet, offering over 100 compatible services on the first day. Vendors that directly integrate MPP—such as Parallel, Stripe Climate, Browser Base, etc.—are marked with a green circle on their cards, indicating they are first-party vendors.
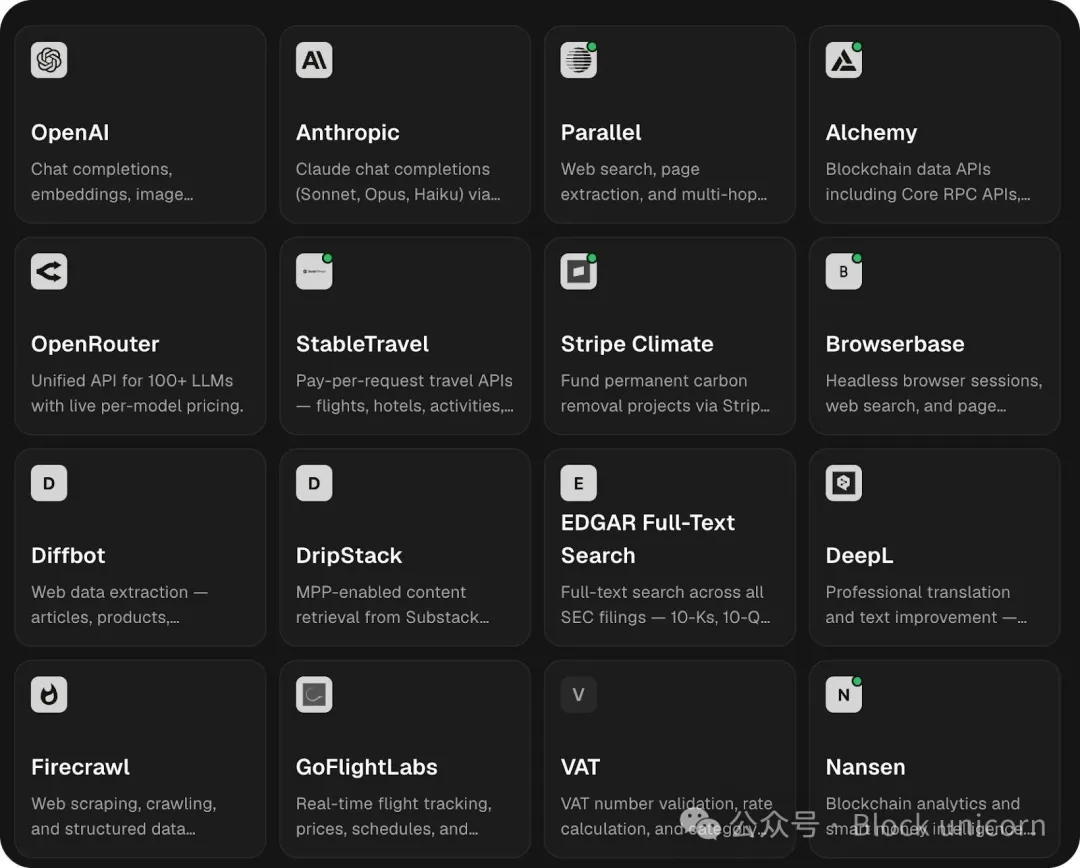
Service directory viewed via mpp.dev
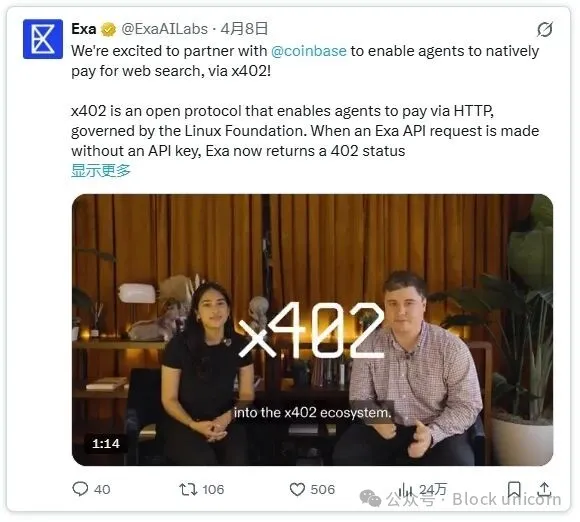
About two weeks ago, popular AI research tool Exa announced native support for the x402 protocol in its search and content endpoints—becoming a first-party vendor and partnering with Coinbase. Exa stated that it chose x402 over proprietary protocols because it is governed by the Linux Foundation.
Inevitable Consequences
Currently, it is impossible to know externally whether an endpoint is first-party, authorized third-party, or unauthorized third-party. This is a solvable problem, and MPP's service directory—which clearly shows the origin of each integration—is a step in that direction.
Unauthorized scraping has already imposed significant measurable pressure on service providers: server load, bandwidth costs, and traffic they never agreed to provide. Third parties wrapping scraped data in the x402 protocol and charging fees only adds insult to injury. Service providers bear all the costs while receiving nothing in return.
Therefore, it is necessary to clarify the root of the problem. x402 is an open protocol—just as developers can build on HTTP, any developer can build on x402. The payment mechanism cannot trace whether upstream data was obtained with authorization. The responsibility lies with the developers who package these endpoints for use.
If there is a lack of accountability mechanisms, it could negatively impact the overall development of x402—potential native integrators might become opponents rather than participants. These revenues rightfully belong to the service providers. Native integration is their way of claiming those revenues, and it is also how x402 gains the legitimacy needed for growth.
Note: As of April 25, Google Flights is no longer listed on Agentic Market.

